Let me say at the outset this is NOT about GenZ bashing.
I work in IT in my other life, all told I am coming up on 50 years since I sat my first computer science class (is anyone using Fortran anymore?). So I have seen a lot, from mainframes to cellphones. Currently I work as a Linux specialist (user / developer since 1994) for a large Canadian microsystems company (hint: these Linux servers run most of the major TV networks around the world).
On a day to day basis I work with new computer engineers and one thing I have noticed about the newest generation is how oriented they are towards clicking buttons instead of keyboarding. That can be a problem in a job where 60% of the time you are deep into a ‘bash box’ running SSH or SFTP or whatever.
One of our most valuable data sources is the packet capture, or PCAP for short. Looking at the actual command traffic between the server and an edge device can be critical in diagnosing networking and configuration issues! For this you can either use a built in GUI app, but for fine-grained data nothing beats tcpdump; but that is command line. See where I am going with this….
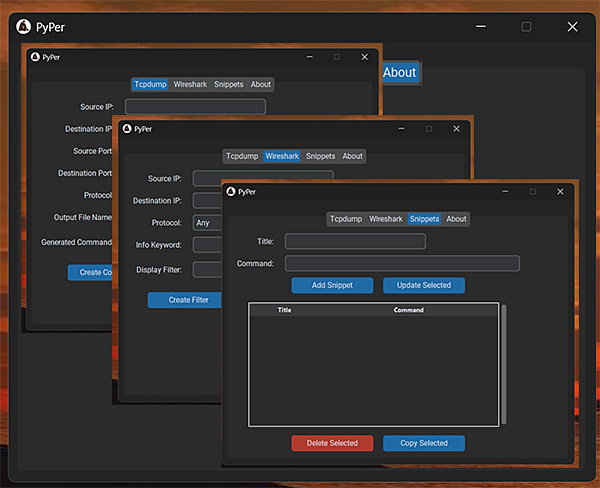
Well, me being me, I set out to bridge the clickety-click gap with an app to generate the tcpdump command so it was a simple copy and paste to get rolling. Along with tcpdump why not create an app to help analyze PCAP’s?
Wireshark is the industry standard for reading PCAP’s, with an excellent display filter system. Soo I built a display filter generator to go along with tcpdump. TFE (too beep-beep easy)!
To complete the divine WAN trilogy I needed a place for folks to store those common bash commands they will use day to day, eg ‘lsb_release -a’ = what version of Ubuntu is running on this server. So I added a simple Sqlite3 db on the backend…
The long and short of it is… PyPer, a tabbed app for tcpdump, Wireshark and saving command snippets.
TFE!
Mark
(With my sincere apologies to Pink Floyd for the terrible pun in the title of this post!)